For Vietnamese businesses, 2026 is the year data protection stopped being paperwork. The Personal Data Protection Law took effect on 1 January 2026, the Cybersecurity Law 2025 follows on 1 July 2026, and Decree 330/2026 has set fines since 19 August 2026. The question is no longer whether to comply, but how far and how.
A new legal framework takes effect
The Personal Data Protection Law 91/2025/QH15 was passed by the National Assembly on 26 June 2025 and took effect on 1 January 2026. It is the first law in Vietnam to regulate the collection, processing, storage and protection of personal data in a comprehensive way, replacing a model governed mainly by decrees. Decree 13/2023/ND-CP of 17 April 2023 used to be the main framework, and is now detailed by Decree 356/2025/ND-CP, effective from the same date, 1 January 2026.
At the same time, the Cybersecurity Law 2025 (116/2025/QH15), passed on 10 December 2025, takes effect on 1 July 2026. The law has 8 chapters and 45 articles, merging the 2018 Cybersecurity Law and the 2015 Law on Network Information Security, and bans the use of artificial intelligence to fake another person's image, video or voice. Decree 330/2026/ND-CP, issued on 19 August 2026, sets administrative fines in cybersecurity and personal data protection, with 4 chapters and 82 articles.
Protection is no longer just the IT department's job
Data protection requirements no longer apply only to banks or technology companies. From recruitment and human resources to marketing and customer care, many everyday activities involve personal data. A business must know what data is collected, where it is stored, for what purpose, who can access it and who is responsible.
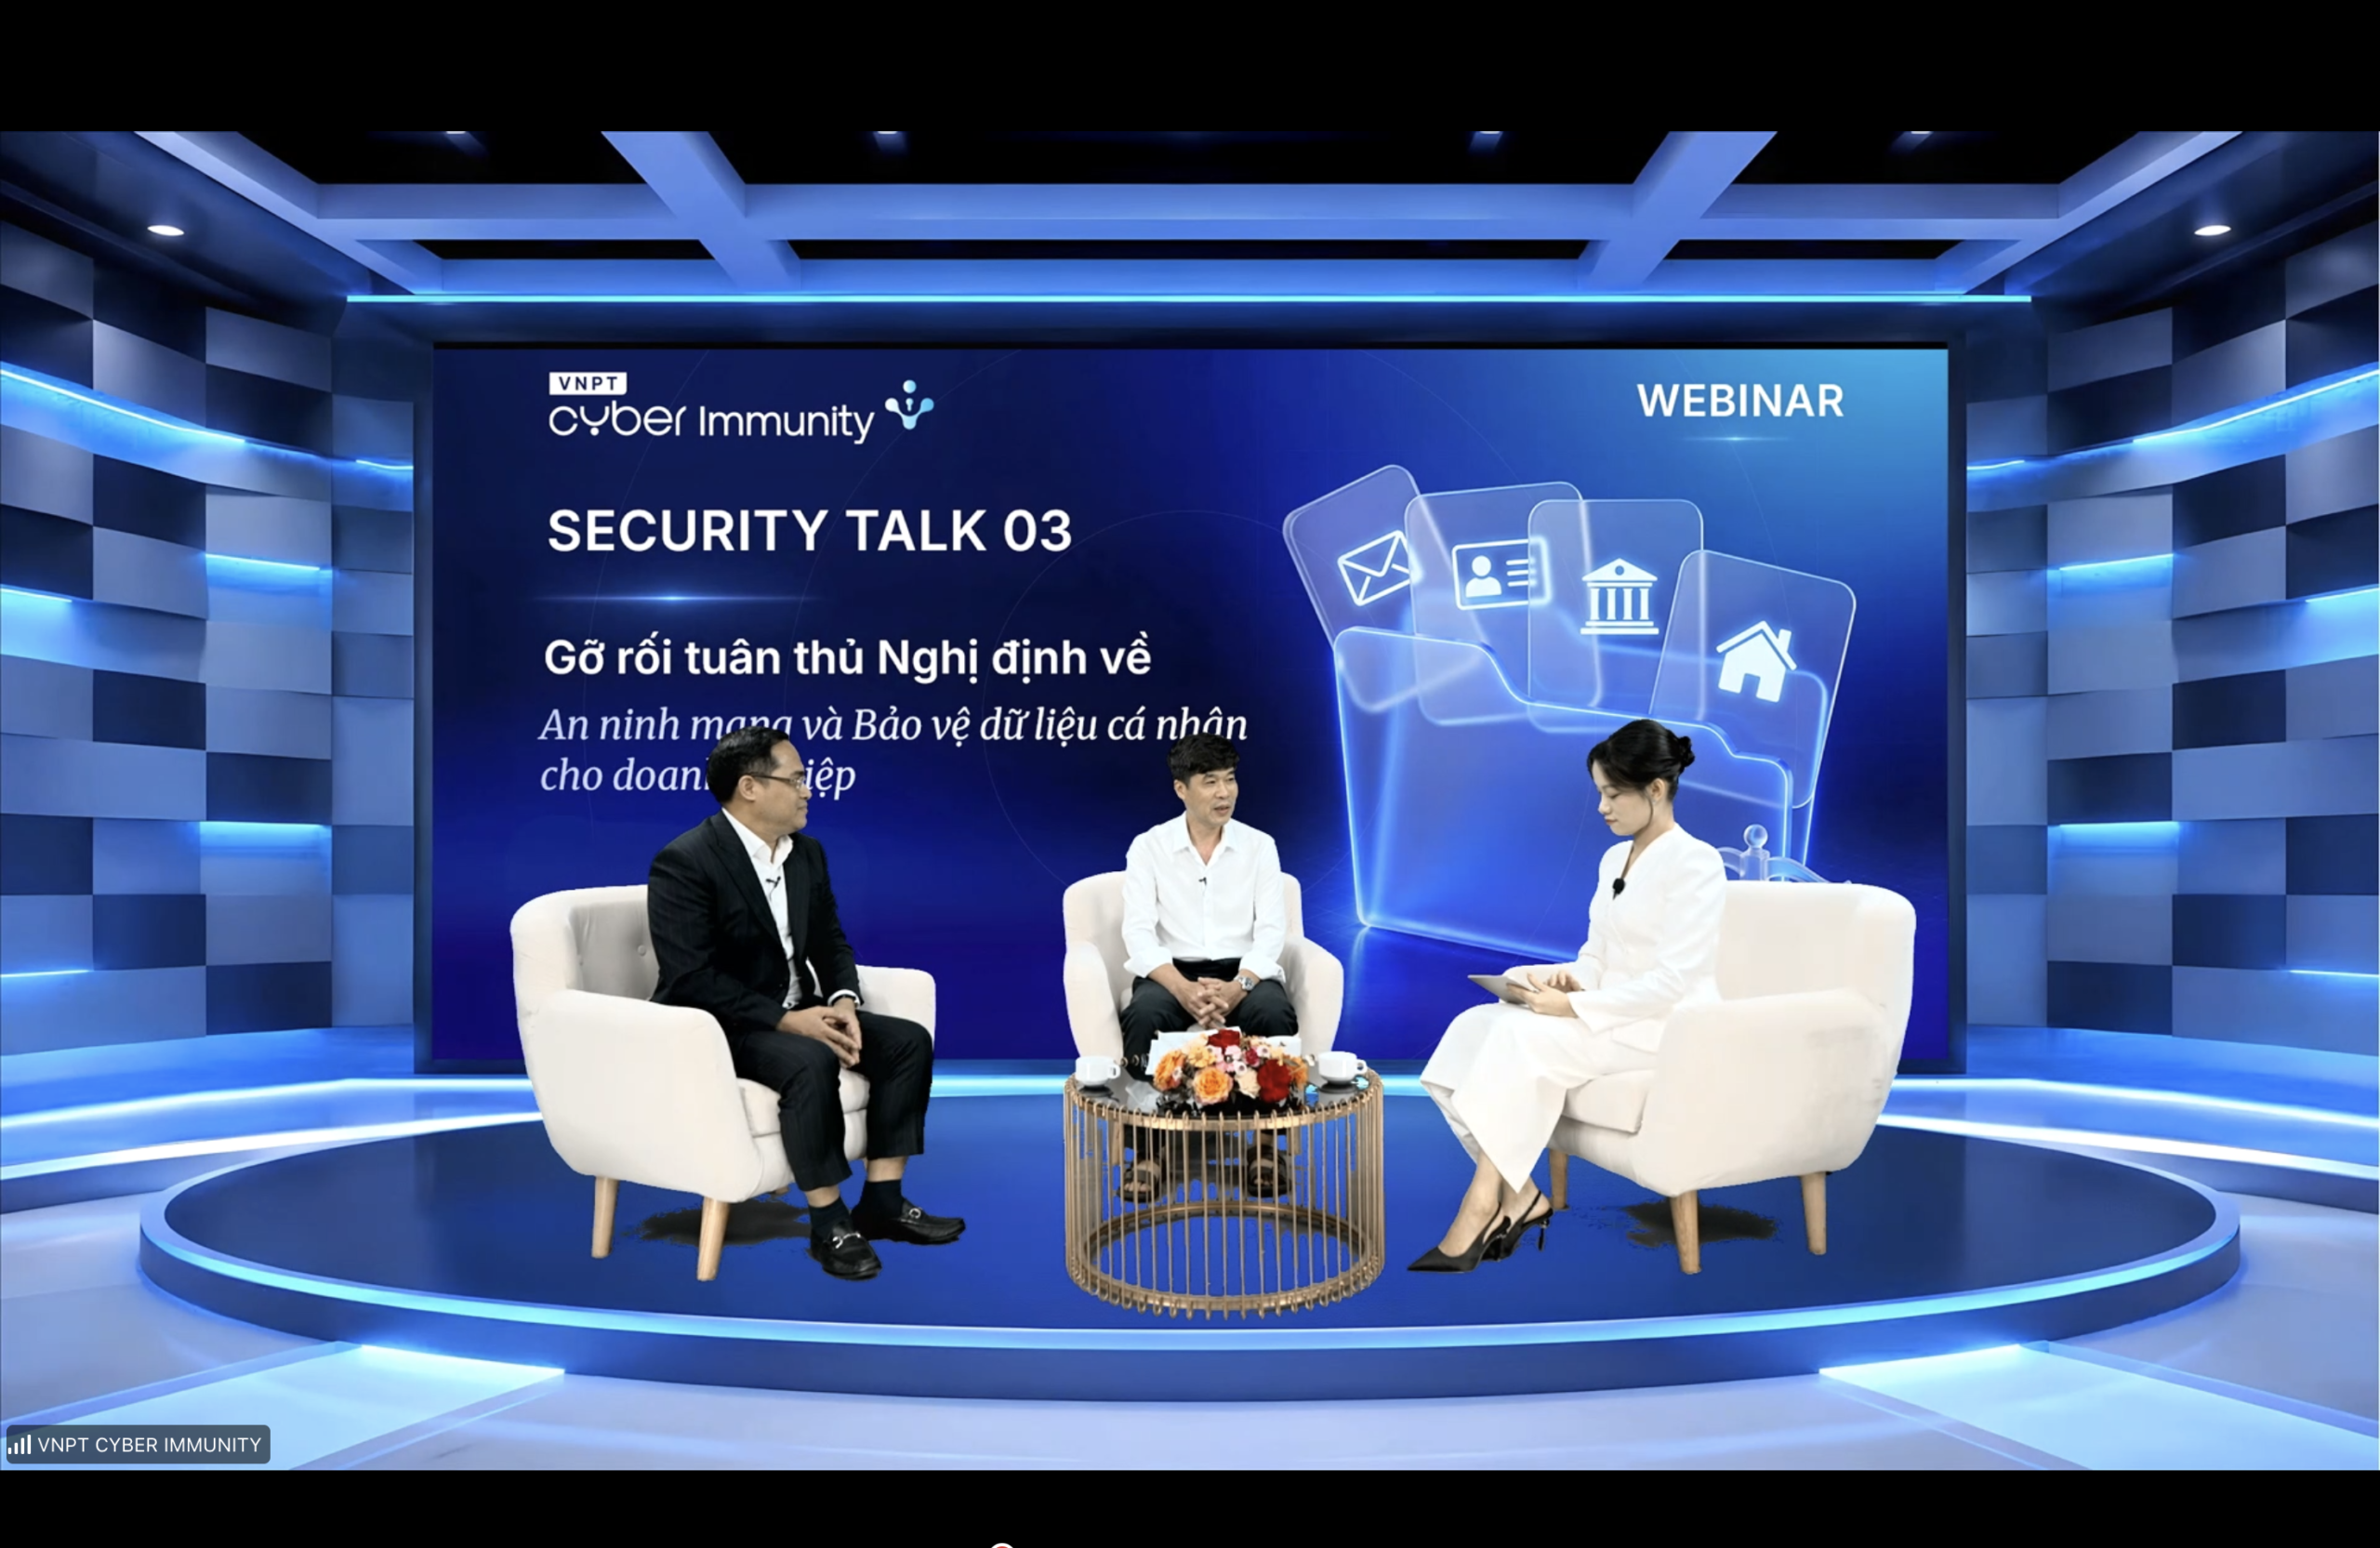
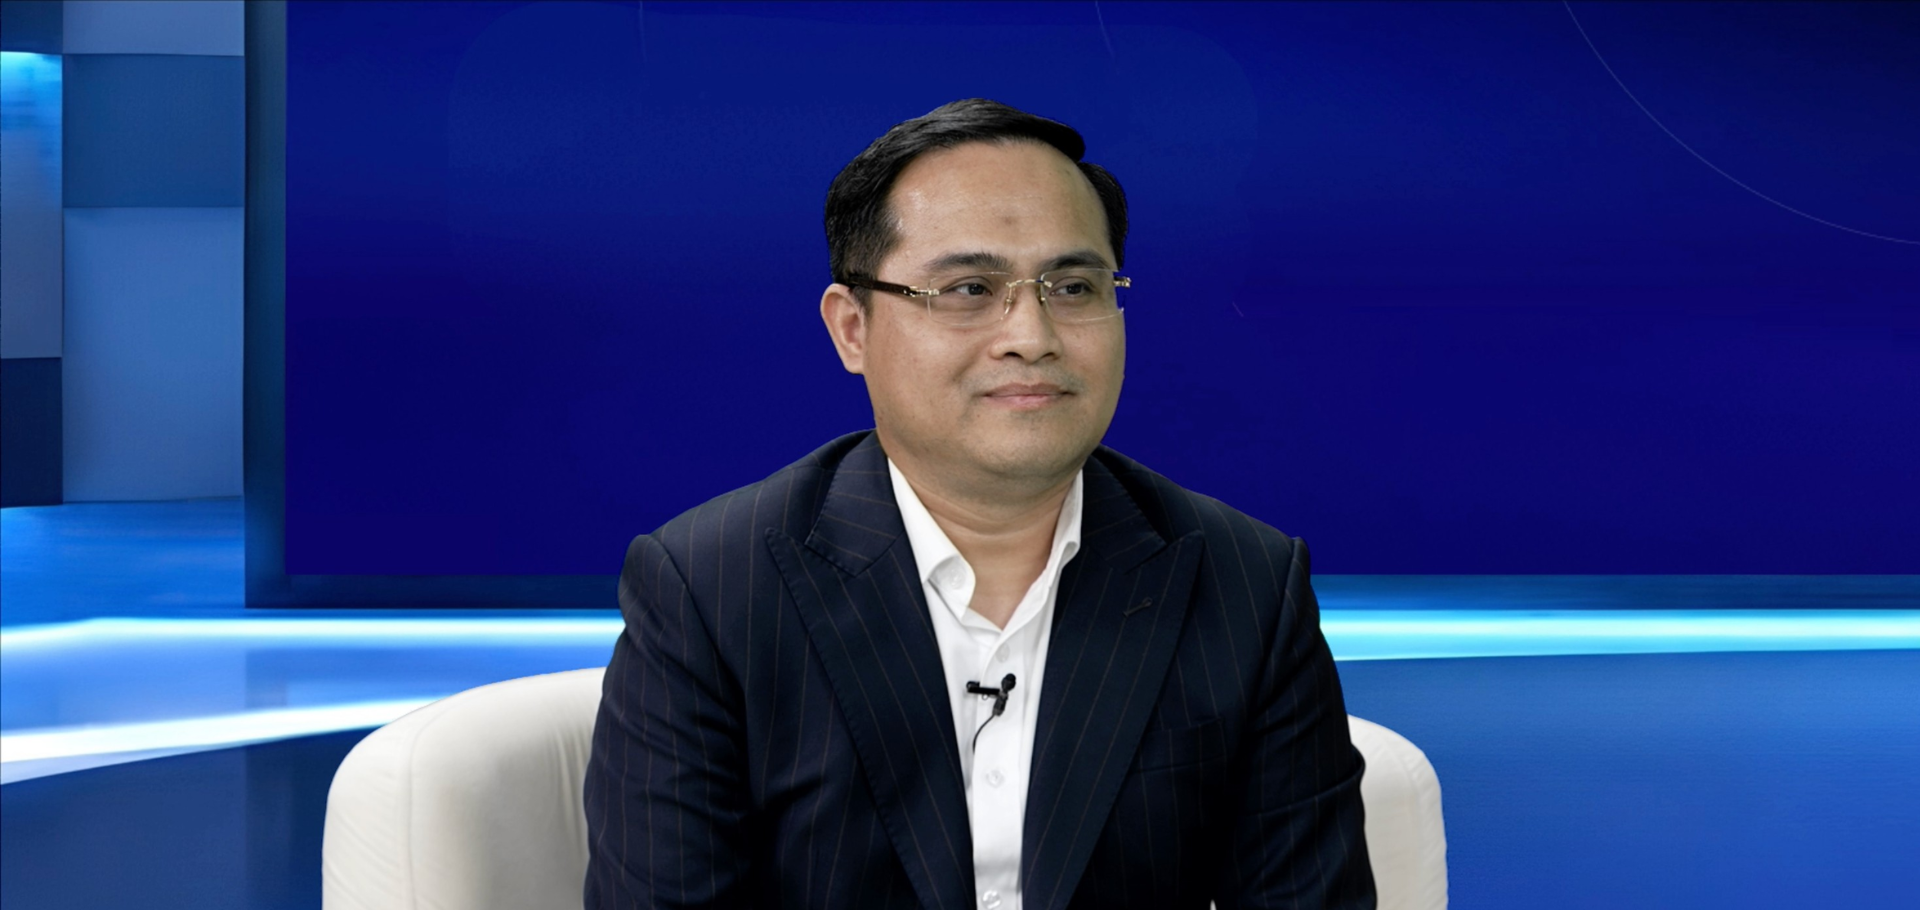
At the Security Talk 03 webinar, Lawyer Luu Xuan Vinh, Founding and Managing Lawyer and Head of TMT and International Arbitration at Asia Legal, set out the obligations businesses need to review: the legal basis for processing, consent and data subject rights, responsible personnel, and impact assessment dossiers. A common gap is the absence of a complete data map to identify processing activities and related responsibilities.
The risk goes beyond fines
The fines under Decree 330/2026 are far from light. For an organization, buying or selling personal data can draw a fine of up to 10 times the illicit gains, unlawful cross-border transfers up to 5% of the previous year's revenue, and other violations up to VND 3 billion. Treating silence as consent to collect and process personal data draws a fine of VND 50 to 70 million, the same band as collecting employee data through cameras or tracking software without clear notice.
But the risk goes beyond fines. Imagine a business discovering that ransomware has encrypted its HR server, with signs that data was stolen. Besides restoring systems and investigating the incident, the business must assess its notification duties, coordinate across departments and control data sharing. A delay or a wrong process can mean operational loss, remediation costs and lost trust from customers, employees and partners.
From passive compliance to protection capability
Another common problem is that businesses cannot find a starting point. Legal handles the rules, IT manages the systems, while Human Resources, Marketing and Sales process data every day. Without coordination, a business can miss obligations or fail to assign responsibility when an incident occurs.
According to Dang Quoc Binh, Process and Compliance Expert at VCI, legacy systems, external services and uncontrolled access rights are notable challenges. Segmentation, encryption, activity logging and anomaly monitoring should match the level of risk. Businesses also need an incident response process, a focal point and a decision maker defined in advance.
Under VCI's advisory approach, compliance should be built into routine governance, with people, process and technology coordinated under leadership direction. The first step is a data map: what data is collected and stored, who can access it, which parties it is shared with, and which risks to prioritize. These documents serve inspections and help a business prove its information security governance when a partner vets it before cooperation, especially in cross-border business. VCI's consulting services support a full security model, ISO/IEC 27001 management systems with NIST as a reference, maturity assessment and security built into product development. Its policy-building service standardizes internal rules, assigns responsibility and sets a unified management mechanism, scoped to each business by size, character and risk level. Compliance cannot be measured by the number of documents completed. When data protection becomes part of governance and operations, a business gains risk control, business protection and customer trust. That is the direction VNPT is taking as it accompanies businesses in a safe and sustainable digital transformation.
Read more
Running Low on E-Invoices? Renew and Top Up VNPT Invoice on OneSME and Save 10%
Sources: Personal Data Protection Law 91/2025/QH15, passed 26 June 2025, effective 1 January 2026; Decree 330/2026/ND-CP, effective 19 August 2026; Cybersecurity Law 2025 (116/2025/QH15), effective 1 July 2026.